AI writes the code. Nobody checks it.
ArgosX independently checks what your AI app builder missed. We find the security flaws, prove how they happen, and give you a fix you can paste right back in. Free scan. No credit card.
Free scan checks your public surface, no card · Pro signs in and uses your app · Compare scan types →
- HIGHDatabase readable while logged outSupabase · public policy
- HIGHService-role key in the JS bundle/_next/static/chunks
- MEDOne user can load another's recordGET /api/orders/:id
- MEDNo confirm on destructive delete/dashboard · Delete all
- LOWMissing security headers (CSP, HSTS)response headers
Real failures in AI-built apps. Each one looked fine until someone outside checked.
170+ Lovable apps exposed
A security researcher found that 170 of 1,645 Lovable-built apps let anyone read, and in some cases write, their database tables, because row-level security was missing or too permissive (CVE-2025-48757, 2025). The apps looked finished. Nothing outside the builder had checked.
Secrets in the browser bundle
In our own scans, 13 live apps shipped a Supabase service-role key in their frontend code: a key that skips every database permission, readable by any visitor.
An AI agent deleted production data
During a code freeze, a coding agent ran a destructive database command against a live app and then misreported what happened (Replit / SaaStr, July 2025). Nothing outside the agent was checking.
Across deep AI + human app scans and automated site-health checks.
The failures a code-scan can't see, caught and proven
Four ways a generated app passes its own demo and still breaks in the wild, and what independent testing does about each. Not a checklist to run yourself, evidence you can act on and show off.
Your database is wide open
Default-public Supabase/Firebase rules are the most common serious leak we find, and service-role keys leaked into your frontend bundle are close behind. We check what a logged-out visitor can actually read and reach, and show you the exact data that's exposed, not just a warning.
One user can read another user's data
Login works, so it looks secure, but the check that says “this record is yours” is the one AI tools forget. We sign in as a second account, pull the first account's private records, and replay the exploit over the real screenshots, then hand you the one-paste fix (or let your AI agent read the findings from our MCP server and patch them in place).
It only works on the happy path
AI builds the demo. Real users hit empty states, bad inputs, expired sessions and edge cases nobody tested. Our AI signs in and uses your app like a customer, and on Human-Verified a person on our team reviews the UX and edge cases automated checks miss.
A trust signal you can show off
Every test produces a VibeScore and a shareable card you can put on your landing page. ArgosX runs from the outside on Lovable, Bolt, Replit, v0 or a custom stack, so the tool that built your app is never the one that signs off on it.
Five dimensions, one score
Every test spans security, functionality, UX, accessibility and performance, rolled into a single VibeScore.
Security & exposure scan
Public database access, leaked AI & service keys (OpenAI, Anthropic, Stripe, SendGrid) in your page and JS bundles, insecure cookies/CORS and missing security headers, the whole exposed surface.
Functional flow testing
We sign in and use your app like a customer: pages, navigation, forms and what each role can reach. We never delete, pay, check out or send messages.
UX & accessibility
Automated checks, plus a person on our team on Human-Verified, catch confusing flows, empty states and a11y gaps.
VibeScore & shareable report
One score across every dimension, a prioritized findings list, and an embeddable trust card for your site.
From URL to trust, and staying there
Paste your URL
We auto-detect your framework and backend, then map what needs testing, before anything runs.
AI + humans test it
85+ AI-driven test scenarios run across security, functionality, UX, accessibility and performance. On Human-Verified, a person adds hands-on checks where judgment matters.
Get your VibeScore
A clear score, worst-first findings with repro steps, and a shareable card, usually within 24–48h.
Keep it that way
Connect your repo and each merge or release is automatically re-checked against that clean report, flagging only genuinely new issues. The re-check looks at just what you changed, so your releases keep moving.
Watch your scan replay, and land on the proof
This is a real ArgosX scan of one of our own apps, replayed step by step over the actual screenshots, ending on a confirmed cross-user data exposure and the one-paste fix. Not a warning, evidence.

This is what your report looks like
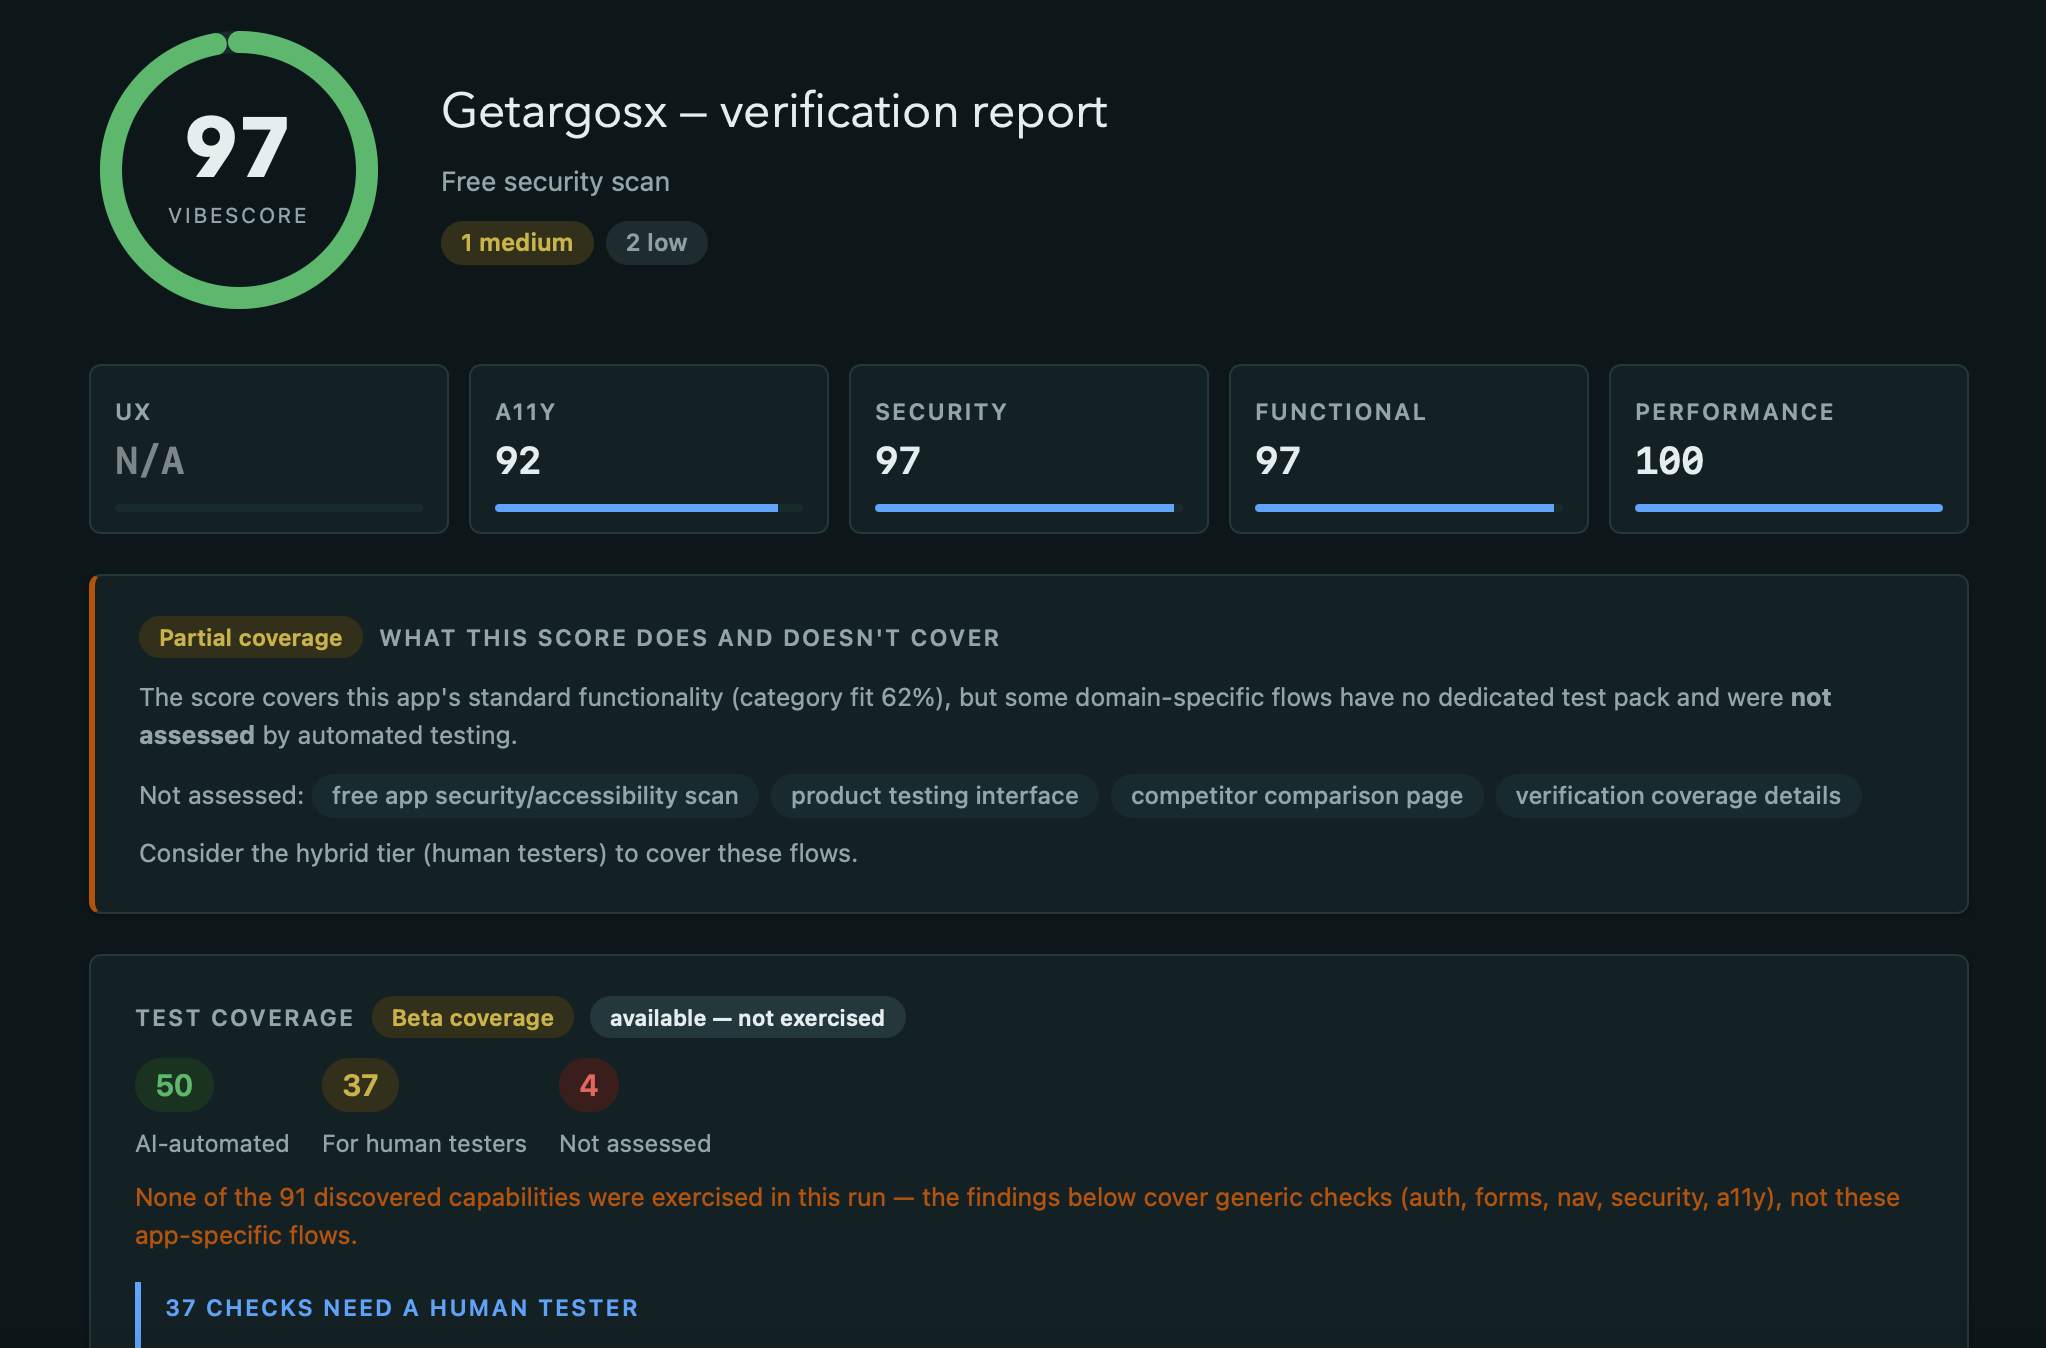
The actual deep scan report ArgosX produced running on itself, the VibeScore, findings, and prioritized fixes in full.
What actually proves your app works
Platform scans and passive checkers read your code. Only real testing proves the app works, and ArgosX does it independently of your builder, whichever AI builder you used.
| Capability | Free scanners$0 | AI test tools$200–1,200/mo | ArgosX Human-Verified$249/scan | Audits & managed QA$500–3K+ |
|---|---|---|---|---|
| Live human testing | ||||
| Functional check (signed-in pages and forms work) | ||||
| No test suite to build or maintain | ||||
| Exploratory (finds unknowns, not just scripts) | ||||
| Independent of your builder | ||||
| Cross-platform (Lovable, Bolt, Replit, v0) | ||||
| Shareable badge | ||||
| Price | $0 | $200–1,200/mo | $249/scan | $500–3K+ |
Compare scan types
Quick and Deep are free and never sign in to your app. Pro and Human-Verified sign in with a test account and exercise everything behind your login, where the real problems hide.
| Attribute | QuickFree | DeepFree | Pro$49/moor $29/scan one-time | Human-Verified$249/scan |
|---|---|---|---|---|
| What it does | Instant check of what any visitor can reach: leaked keys in your page and bundles, an open database, missing security headers | Crawls up to 15 logged-out pages: security headers, cookies, TLS, accessibility, SEO, broken links, pages a stranger shouldn't reach, and leftover placeholder text or missing-space typos | Everything in Deep, plus we sign in with your test account and use the app like a customer, forms included, with a second sign-in role | Everything in Pro, plus a person on our team for the judgment calls software can't make |
| Signs in to your app? | No | No | Yes | Yes |
| How long | Instant | Under 2 min | 30–60 min | + human pass, ~48h |
| Price | Free | Free | $49/moor $29/scan one-time | $249/scan |
Most builders want a Pro AI scan. It's the only tier that gets past your login, where most real problems live. Give us a test email + password account so we can sign in. How to enable email + password login on Base44, Bolt & Replit →
Start free. Upgrade when you're ready to launch.
Free scans to start, a monthly Pro plan when you launch, and a pay-per-scan human-verified tier. Your exact scope is computed after we explore your app.
- Leaked AI & service keys (OpenAI, Anthropic, Stripe, SendGrid) in page + JS bundles
- Open-database check: data a logged-out visitor can read
- Security headers, cookies & TLS
- Accessibility, SEO & broken links
- Logged-out access probe, no signup, just your email
- Everything in Free scan
- Signed-in use of your app: pages, forms, roles
- Tests each sign-in role you give us
- Accessibility sweep
- VibeScore + shareable card
- Scan runs 30–60 min · report in ~24h
Safe testing: we never enter real payment details or move real money in your app.
- Everything in Free scan
- Signed-in use of your app: pages, forms, roles
- Tests each sign-in role you give us
- Accessibility sweep
- VibeScore + shareable card
- Scan runs 30–60 min · report in ~24h
Safe testing: we never enter real payment details or move real money in your app.
- Everything in Pro AI scan
- A person on our team reviews it hands-on
- UX & edge cases
- Shareable Human-Verified badge
- Results in ~48h
- AI re-check of your fixes: $29
Safe testing: we never enter real payment details or move real money in your app.
Before you run the scan
Do I actually see the vulnerability, or just a description of it?
You see it. For access-control bugs, the kind where one signed-in user can read another user's private data, ArgosX doesn't just describe the risk, it reproduces it: we authenticate a second, separate account and replay the exact request that pulls the first account's data. Then we play that scan back to you step by step over the real screenshots, ending on the confirmed finding and a one-paste fix. There's a replay of a real one on our home page. Proof you can watch is worth more than a warning you have to take on trust.
Why can't the AI that built my app just test it too?
It's grading its own homework. The same model (or a sibling model) that wrote the code shares its blind spots. If it didn’t think about an empty state, a race condition, or a leaky Supabase rule while building, it usually won't spot the same gap while reviewing. ArgosX is a separate, independent AI that has run automated scans on more than 13,000 other apps and the failure patterns they share, patterns it never touched during your build, plus a human tester for the judgment calls no model makes well. Independence plus breadth is what catches what your builder can't see in its own work.
What's the difference between the free scan and a paid test?
Short version: the free scan (Quick and Deep) never signs in to your app, so a test login isn't used there. Only the paid Pro and Human-Verified tiers sign in and test what's behind your login.
The free scan has two parts, both read-only. The instant check looks for keys leaked into your page source. The deep free scan then crawls what any visitor can reach, security headers, cookie and TLS settings, accessibility, SEO, broken links, whether a logged-out visitor can open pages they shouldn't, and whether any of your data is readable without signing in at all.
The paid tiers actually drive your app end-to-end, signing in, submitting ordinary forms and checking what really happened, and exercise the flows behind your login, which no free scan touches because driving a live app needs your authorization.
What does each scan level actually do?
Quick (free): an instant check of what any visitor can reach: keys left in your page and bundles, whether your database answers without a login, and missing security headers. No sign-in, nothing clicked.
Deep (free): we open your site like a visitor would and walk up to 15 pages, checking security settings, cookies and certificates, accessibility, SEO, broken links, whether a logged-out stranger can open pages meant for members, and whether any of your data is readable without signing in. We also flag unfinished-looking content on those pages: leftover placeholder text (lorem ipsum, “coming soon”) and words run together by a missing space. Takes less than two minutes.
Pro ($49/mo): everything in Deep, plus we sign in with a test account you give us and use your app like a customer: navigating, filling forms, submitting them, and checking what really happened afterwards, plus whether one user can reach another's data. We never delete, pay, check out or send messages. A Pro AI scan typically runs 30–60 minutes, and up to 90 for a large app with a second sign-in role.
Human-Verified ($249/scan): everything in Pro, and then a person on our team works through the judgment calls no software makes well, hands-on and read-only: whether a flow makes sense, whether it feels trustworthy, what happens when a session expires.
Every report tells you what we checked and, just as importantly, what we couldn't reach and why.
Is the Human-Verified badge really checked by a person?
Yes. After the automated pass, a person on our team works through UX and edge cases hands-on and confirms the flagged findings, the things that need human judgment, like whether something merely runs versus actually feels trustworthy.
How long does a test take?
Two different clocks, and it's worth separating them.
The scan itself: the quick free check is instant, the deep free scan takes less than two minutes, and a Pro AI scan typically runs 30–60 minutes, up to 90 for a large app with a second sign-in role, because we're genuinely driving it rather than reading it.
Then the wait for your report: we review Pro reports before releasing them, so they usually land within 24 hours, and Human-Verified adds a real tester's pass and usually lands within 48. You don't need to keep the tab open. We email you.
What if you can't sign in to my app?
We tell you, on the report, instead of quietly scanning less. A Pro AI scan uses the test accounts you give us, and we try each sign-in several times before giving up. A login can fail for reasons that have nothing to do with your app, like a deploy landing mid-scan.
But if a role still won't sign in, everything behind that login goes untested, and the report says exactly which role we couldn't reach. This matters more than it sounds: a scan that quietly covers less looks identical to a clean result, and the score would drift for a reason you'd have no way to see. We'd rather show you a gap than a flattering number.
My app has more than one kind of user. Can you test two sides of it?
Yes, and it's worth doing. Give us a second test account, a seller alongside a buyer, say, or an admin alongside a member, and we sign in as both and test what each side can actually reach. Most of the interesting problems live at the boundary between two roles, and a single-account scan can't see them by definition. Each side's findings are labelled with the role they came from, so you know who is affected.
My app only has Google or social login, no email/password. Can you still test the signed-in area?
Yes, by handing us a session instead of a password. Since there is no email/password for us to type, you log in once in your own browser and give us that already-signed-in session to reuse.
It takes about 30 seconds: sign in to your app as normal, open your browser's developer tools (F12, or Cmd+Option+I on a Mac) and click the Console tab, then paste this one line and press Enter, which copies the session to your clipboard:
copy(JSON.stringify({url:location.href,cookies:document.cookie,localStorage:{...localStorage},sessionStorage:{...sessionStorage}}))
Send us the result (or paste it into the session box in your app's setup) and we do the rest.
Two things to know: the session is short-lived, so grab it close to when the scan runs, and the console capture can't read HttpOnly cookies, so if the signed-in scan comes back looking logged out we'll ask for a Playwright storage-state export instead. If your app also offers email/password, that's simpler and doesn't expire, so prefer it.
Do you store or touch my data?
The free scan is read-only and needs no account or card, just an email to send the report to. Paid tests sign in and use your app like a real user, so they can create and change records: point us at a test account. They never delete, pay, check out, upload files or send messages.
If issues are found, do I have to pay again to check my fixes?
Not necessarily. Once you've shipped fixes, a $29 AI re-check confirms what the AI found, without a second full price. A full human re-test is a new Human-Verified pass ($249).
Find out what your app is hiding, in under two minutes.
Run the free scan now. No signup, no card, nothing deleted or changed.