Security isn't a launch-day checkbox. It's your next retainer.
Your AI tooling lets you deliver client projects in days, not months, and then those apps keep changing. ArgosX watches every client app after the handoff: when a commit introduces a new security issue, the alert comes to you, so your team fixes it quietly instead of hearing about it from the client. And every month there is co-branded, independently verified proof to send, which is what turns "trust us" into a line item they renew.
Free scan in under two minutes · no credit card · read-only
Speed shifts the risk onto you
The client isn't reading the code. They're trusting that the team who shipped it also checked it.
A real ArgosX scan replay on one of our own apps, landing on a confirmed cross-user data exposure.

You're the last set of eyes
The AI builder wrote the app, and it demos well. If nobody outside that loop reviews it, your name is still the one on the invoice when something breaks.
One leaked project is one lost client
An exposed database or a key sitting in the JS bundle doesn't stay quiet for long. It becomes a support ticket, a bad review, or a contract that doesn't renew.
"We checked" isn't verifiable
Without a third-party result, your assurance is just a sentence in an email. Clients increasingly want to see it, not just hear it.
Scan before you deliver, not after a client finds out
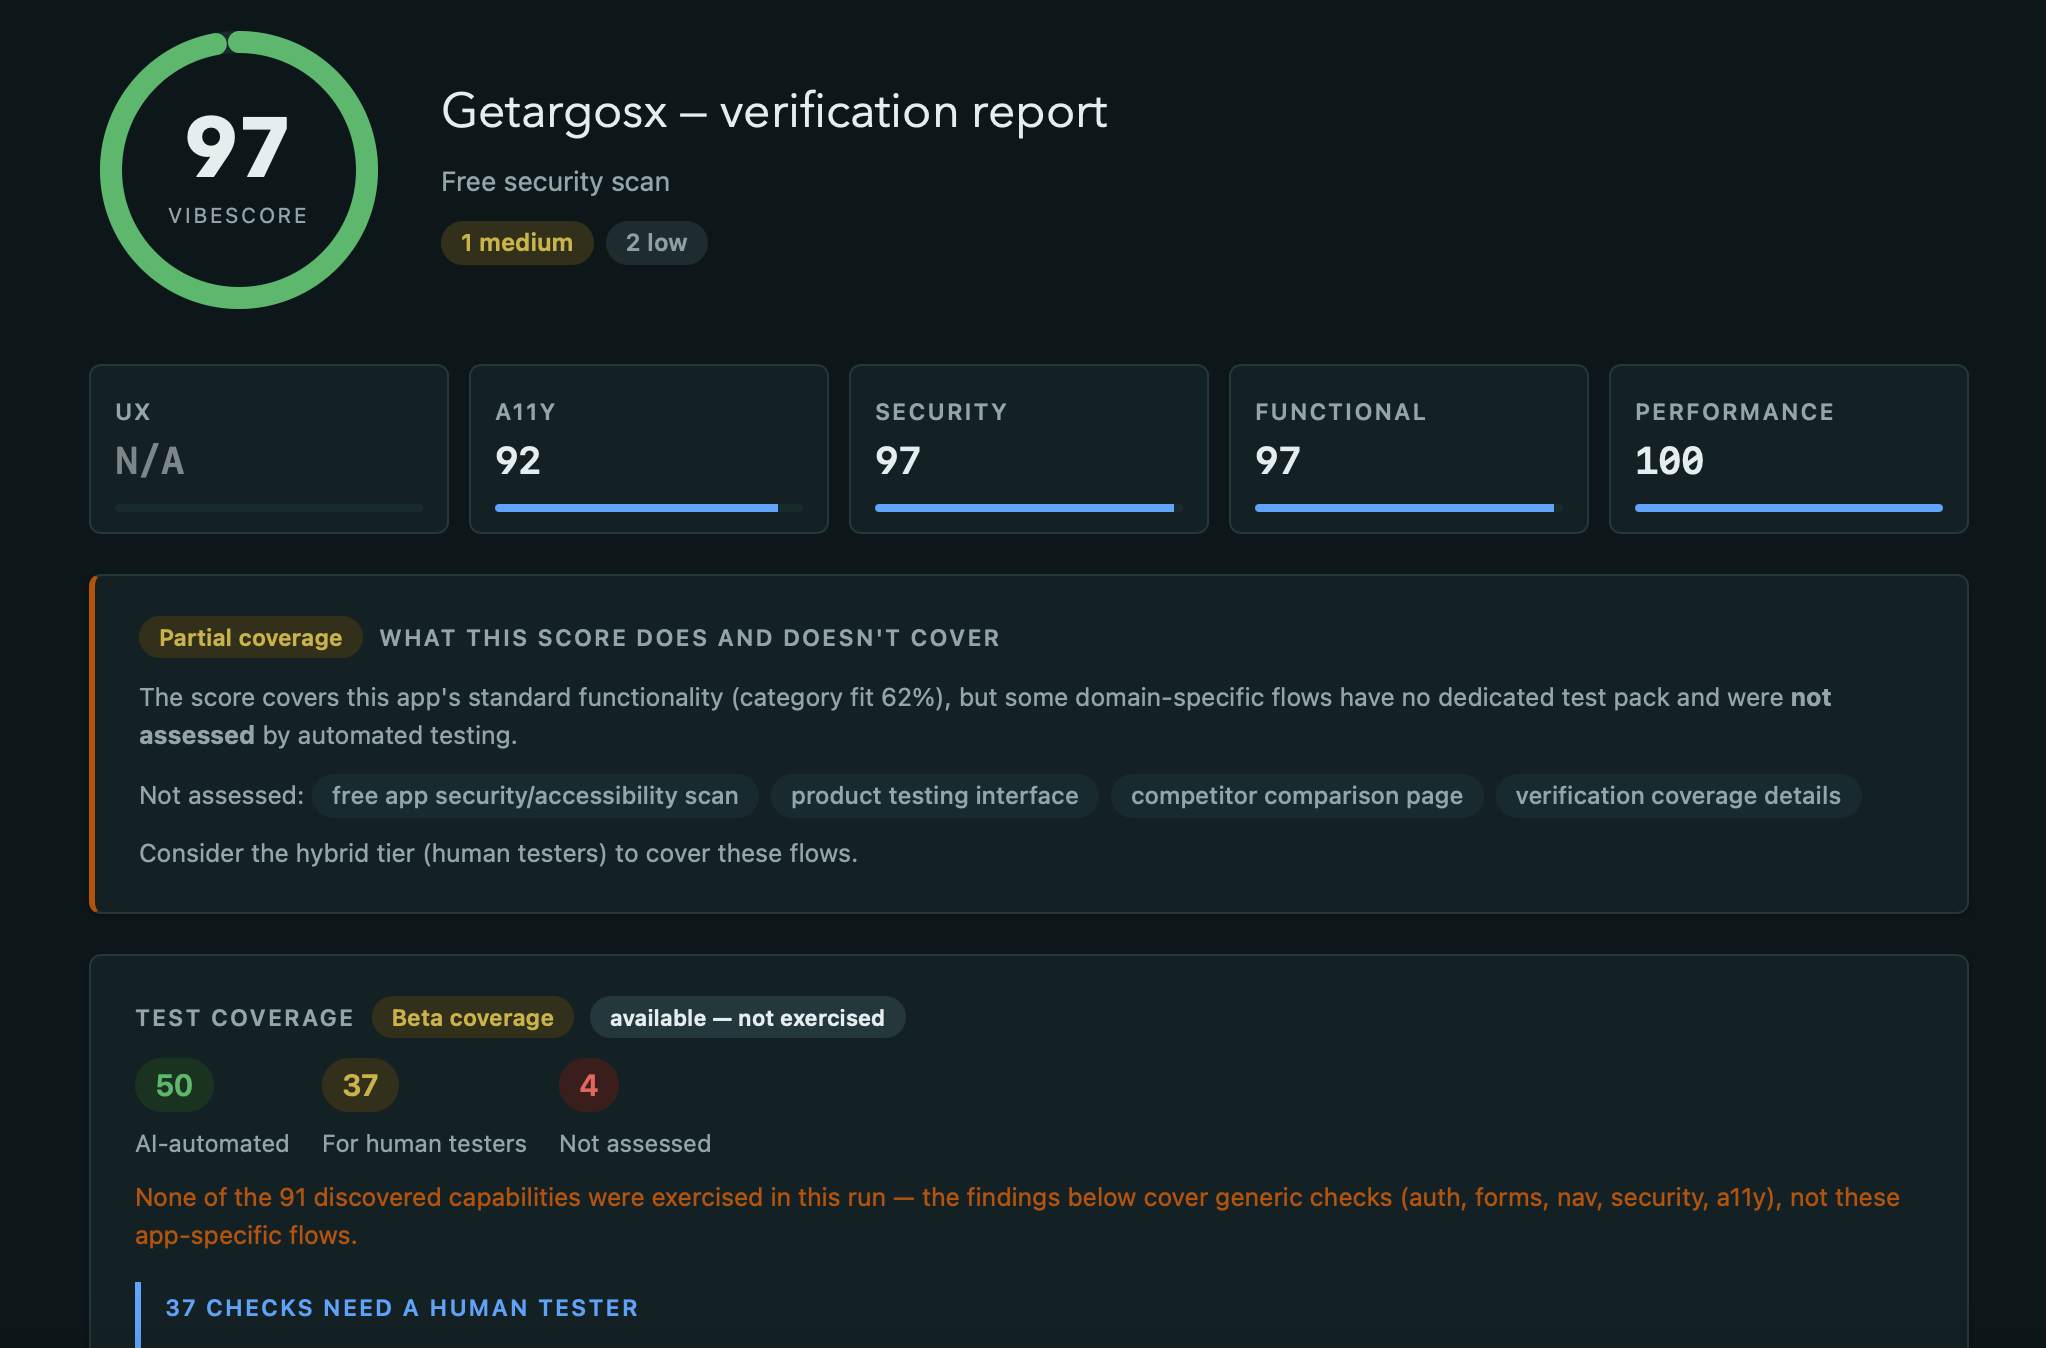
What your client gets: the actual report, worst-first, with a fix they can paste.
The first scan sets the baseline
Paste the URL and we explore the app the way a real user and an attacker both would: navigation, forms, auth, the works. That clean result becomes the baseline every later commit is measured against.
A report the client can actually read
Every finding comes worst-first with severity, location and repro steps, plus a fix prompt your team can paste straight into the builder that made it.
A VibeScore the client keeps
Hand over a clean result as a shareable badge, so the client has independent proof the work was checked, not just your word for it.
The builder that shipped it can't grade its own work
Same blind spots, every time
AI tools tend to repeat the same handful of mistakes: open databases, missing ownership checks, secrets in the bundle. A separate pass catches what the builder's own review can't.
A human pass where it counts
For higher-stakes client work, add a human-verified review on top of the automated scan, for the projects where you want more than a machine's word.
Reusable across every client
The same independent layer works whether the app was built in Lovable, Bolt, Cursor, v0 or Replit, so you run one process across your whole pipeline.
Catch the regression before your client does
AI-built apps change fast, so a one-off scan ages out in a week. Wire ArgosX into each client repo and every push is re-checked automatically, with the alert coming to you, not to your client.
A gate on your releases
The ArgosX GitHub Action re-attests the deployed app on each push and fails the build only on NEW security defects, so an accepted issue never blocks the pipeline but a fresh broken-access or data-exposure bug does. Being straight about the trade-off: because we sign in and drive the app, that check takes tens of minutes, so we recommend running it on merges and releases rather than on every push.
You hear about it first
When a commit introduces a new gate-worthy finding, ArgosX emails you, the agency, so you fix it quietly before the client ever notices. One key per app, so a leak in one client's repo can never reach another.
One dashboard, real trends
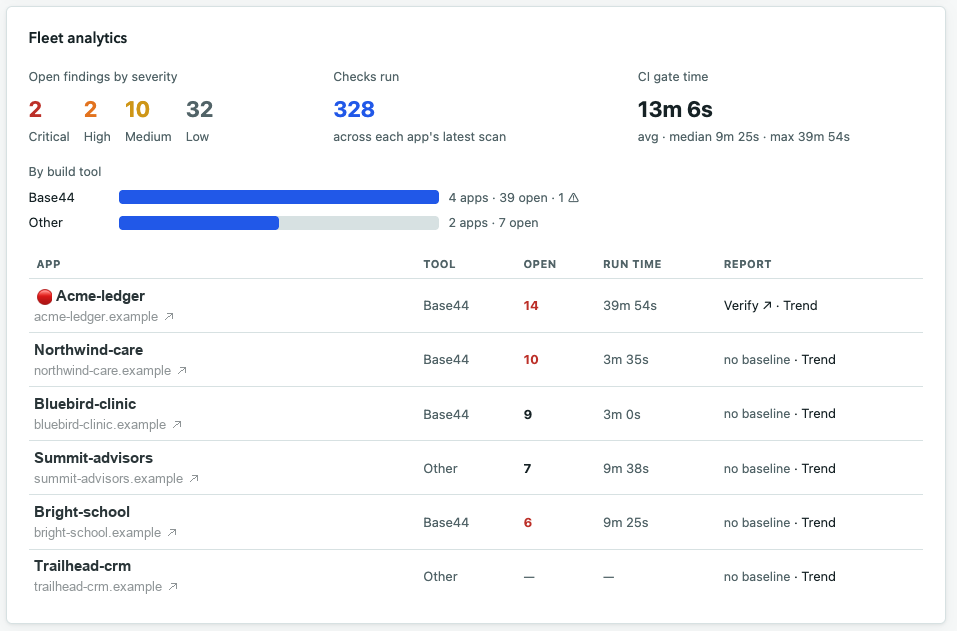
Your fleet view shows every client app's status, findings by severity and by AI tool, scan run-times, and a week-over-week new-vs-fixed trendline you can put straight in front of a client. Per-app trend pages show a client exactly how their app got safer while you had the retainer.
A refactor doesn't reopen fixed bugs
AI tools rewrite files constantly. We track a flaw by what it is, the kind of failure, the endpoint and the data it exposes, not by the file and line it sat on. Move the code and the finding follows it, instead of flooding you with duplicate alerts for issues you already fixed.
Turn AI security fears into a billable retainer
Your clients already know AI-generated code leaks data and breaks authorization rules. ArgosX gives you co-branded, independent attestations showing exactly what was tested and what passed: close nervous prospects, then justify the monthly maintenance fee with an artifact the client expects, at zero extra engineering overhead. Flat monthly rate by active app count. Co-branded, not anonymous: reports carry your brand alongside “independently verified by ArgosX,” which is the third-party trust your client is actually paying for.
Security and pen-test firms can use the $299/mo Growth tier as a Partner plan.
- One dashboard for your whole client fleet, so you always know which apps are solid and which need action before a client asks
- A check on every merge or release, with the alert coming to you first, so you fix issues quietly before the client ever notices, and each client's access kept fully isolated from the rest
- Co-branded security reports and an “independently verified” badge, the proof that justifies your monthly retainer
- Branded security baselines for prospects, so you walk into every pitch with evidence instead of promises
- Human-verified review on demand, for the client work where you want more than a machine's word
We onboard every agency partner one-on-one, so your fleet dashboard and reporting are set up with you from day one.
Start with one client app. Keep it protected from there.
No signup, no card, nothing changed or deleted. Paste the URL and see what we find.